How Do Helpful Features Create Privacy Risks in Apps?
Some convenient features create privacy risks in apps when they require access to data or introduce a new data flow outside the app’s original security boundary. Some cases in point are contact discovery that may process your address book to match users, link previews may make network requests to retrieve content from an external website, cloud backups may create additional copies of messages outside the app’s primary encrypted storage, and automatic saving may transfer protected content into ordinary device storage. The app privacy impact depends on what data the feature handles, where that data is processed or stored, who can access it, how long it is retained, and whether the user or provider controls the encryption keys.
Developing this idea, some of the biggest privacy risks in apps don’t look as threatening as privacy problems, and users could not see them as such because they are in every app and are convenient. Something that saves you time because the app remembers what you did before and recognizes what you need without asking. A little automation that takes another step out of your hands and makes everything feel effortless.
And we see this everywhere now. Apps connect to third-party services to translate, preview, analyze, store, synchronize, recommend, or process things for us.
One thing worth understanding is that the features are in the app, but behind that there may be another service accessing information, another system processing it, or another copy being created somewhere outside the conversation. Even if we visit a site, data is somehow tracked unless it is privacy-focused.
Adding to this, these features are worth looking at closely, especially through the lens of privacy by design.
If a private messaging app is truly private, it should be clear about what it protects and what it will not give up just to make things easier. Small choices that seem harmless at the time might slowly give your information more places to go.
What Convenient Features Create Privacy Risks in Apps?
Many convenient features can create privacy risks in apps when they need to do a lot in the background, such as access, copy, process, or share information beyond what the core feature requires.
Apps are full of these small conveniences. They make things faster, remember things for you, and remove little bits of effort from your day.
Let’s go through the friendly little features one by one, and you will recognize every single one.
And notice something as we go: none of these features has to be malicious. That is what makes them interesting. A product team can build them because they genuinely want the product to feel easier to use. The app privacy problem begins when the easiest path for the user also becomes the easiest path for collecting information, creating copies, opening connections, or removing security barriers.
Thus, “Helpful” describes how a feature feels. It tells you almost nothing about what the feature has to do behind the scenes.
“We noticed your friends are already here!”
Feels great, right? You install something, and suddenly it is already filled with people you know. The empty room problem is gone. Nobody wants to join a private messaging app only to find a lonely space with no one to talk to. Instead, there is an instant community waiting for you.
Now ask how it did that, because there is no privacy by design. It went through your entire contact list; every name, every number, every person you have ever saved, including people you would have forgotten you had, and checked all of them against its records. That warm welcome was powered by you handing over your whole address book. And here is the kicker: it is not just your privacy you gave away. Every person in your contacts just got their number checked by a company they never chose, because you installed something. You volunteered your dentist, your relatives, your kid’s school, your landlord, and the same goes for our contact in someone else’s phone, which neither of us ever agreed to.
Furthermore, there is a technical detail here that is easy to miss: contact discovery does not magically become private just because an app calls it “finding friends.” The important question is what information leaves your device, whether it is transformed or hashed, whether the service can retain or correlate it, and whether the company can learn relationships from repeated lookups. “We only use your contacts to find friends” is not the same thing as “your contacts never leave your control.”
And there is a second privacy boundary hiding underneath it. Your address book is not just your data. It is a database you created about other people. Their numbers, names, relationships, workplaces, family members, and old contacts may all be sitting inside it. Giving an app access to that database can expose information about people who never installed the app at all.
“Tap this link right in the chat!”
It is so convenient that someone sends you a link, you tap it, and it opens. Why would that be a problem?
Because the moment you tap a link, the place it takes you can often see where you came from. It gets a little note that says “this person arrived from that app.” Which quietly confirms you use that app, and hands a stranger’s website a thread connecting your tap to the private place you were just in. A convenience feature turned into a little leak, and you would never know, because tapping a link is the most natural thing in the world. An app that cares about your privacy might make you copy the link and open it yourself. That tiny extra step keeps the website more separated from the private conversation you came from.
We see almost every app pick convenience.
The deeper lesson is that app privacy can disappear at the boundary between two systems. Your private conversation may be protected inside one private messaging app, but the moment an action hands something to a browser, website, operating system service, analytics SDK, or another application, a different set of rules can apply. Encryption inside the chat cannot automatically protect what happens after the data leaves that boundary.
This is why privacy has to be evaluated as a whole system (privacy by design), not as one impressive feature. “The messages are encrypted” can be technically true while the surrounding features still create information leaks.
“Back up your chats to the cloud!”
This one sounds like pure responsibility. Protect your precious messages! Never lose anything with these privacy features!
But stop and think about what a backup is. It is a complete copy of all your private conversations, taken out of your phone and parked on a system somewhere else that you don’t control. Everything you were careful about inside the app is elsewhere the moment it is copied off to a backup, because that backup usually doesn’t have the same protections at all. You built a vault and then photocopied everything inside it and left the copies in a storage unit across town. And that storage unit can be hacked, handed over, or quietly read in ways the original never could. The “helpful” backup is often the single leakiest thing about the whole setup, the soft underbelly behind the strong front.
The difference may seem small, but it changes the outcome between an encrypted backup and an end-to-end encrypted backup. Encryption by itself does not tell you who holds the keys. If the service can decrypt the backup, then the service is still technically capable of accessing the contents. If only you and the intended participants control the keys, the provider has a very different security boundary.
“Save this photo to your camera roll!”
Someone sends you a picture, you save it, done. But once it is in your regular camera roll, it is just a normal photo again, backed up to the cloud, scanned by whatever scans your photos, synced across your devices, totally outside whatever protection it had inside the private messaging app. The careful little world the app built around that image evaporates the instant it lands in the general photo pile.
The same principle applies to files, documents, voice recordings, screenshots, and anything else that crosses from a private messaging app into ordinary device storage. The moment a protected object becomes an ordinary operating system file, its privacy depends on the operating system, your backup provider, other applications with access to that storage, and whatever automated processing happens there.
A genuinely privacy-conscious design therefore treats exporting as a security boundary and is aware of such privacy risks in apps.
“We will remember you so you don’t have to log in!”
Lovely! No annoying re-typing. Except “we will remember you so you never have to unlock” is the same sentence as “anyone who picks up your phone never has to unlock either.” The convenience of never being challenged is identical to the danger of never being a barrier. Every bit of friction you removed for yourself, you also removed for whoever grabs your phone. The app made your life easier and a thief’s life easier by the same amount.
Security often works through friction. A password, PIN, biometric prompt, session timeout, device lock, or reauthentication step is annoying precisely because it interrupts whoever is trying to get through. Remove every interruption, and you have not created “better security.” You have simply created a smoother path to the account.
Convenience and security are not always enemies, but pretending they are always aligned is dangerous.
“Add a little animation, a link preview, a fun extra!”
All the little flourishes that make chat feel rich, such as the previews, the auto-loading images, the fun file types, GIFs – each one is a little door that has to open something from outside to work. And doors that open things from outside are exactly how nasty stuff sometimes sneaks in. The plainer, more boring app that doesn’t auto-open every clever thing is often the safer one. But boring doesn’t demo well, so apps keep piling on add-ons, each a tiny new way in.
This does not mean every preview, animation, or rich media feature is automatically dangerous. It means every automatic action deserves an audit, particularly what code is running, what resource is being contacted, what information is being sent, and what happens before I have chosen to open it.
Security engineers think about this in terms of attack surface. Every parser, renderer, network request, file format, integration, and external dependency adds something that has to behave correctly. More functionality can mean more ways for something to fail. A feature can be delightful for the user and still increase the number of things the security team has to defend.
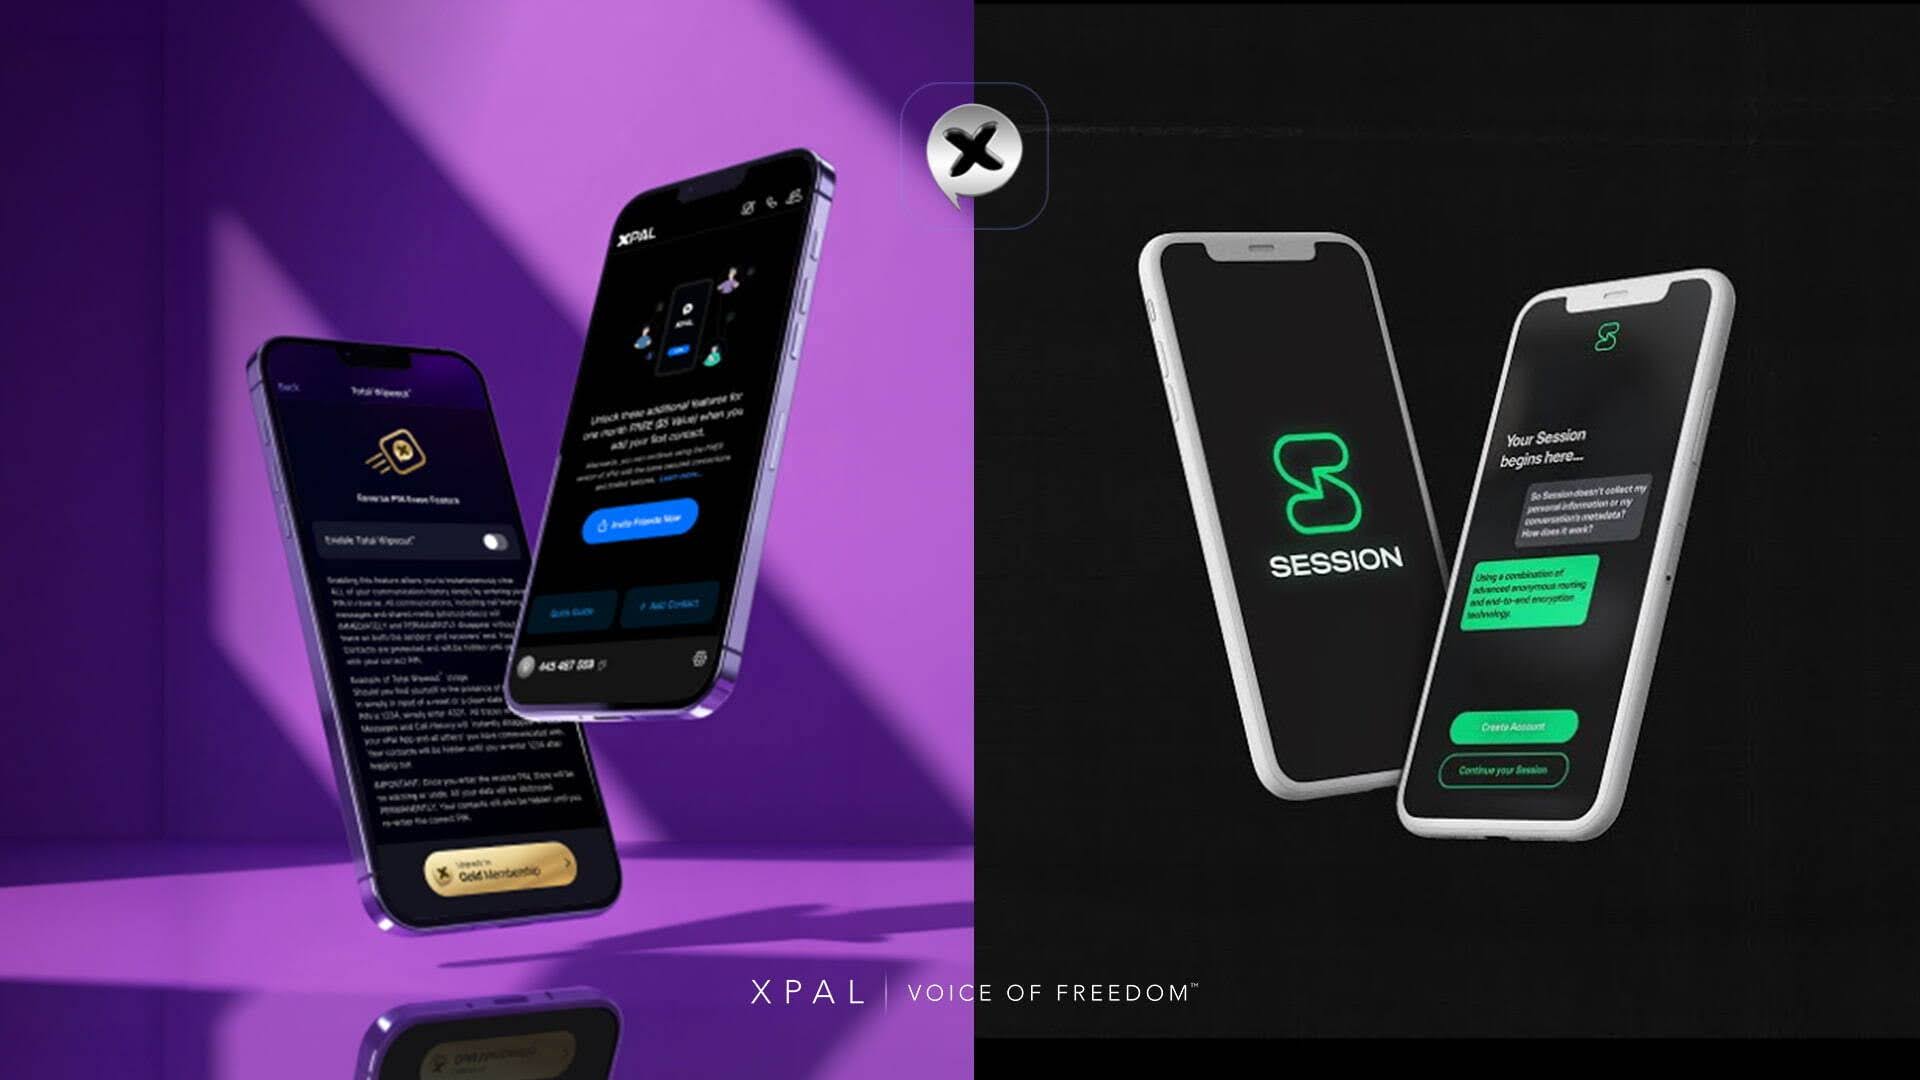
The situation becomes more complex when people compare privacy apps by screenshots and feature lists and simple convenience. Two apps can offer the same feature while making completely different architectural choices underneath it. One might process something locally on your device. Another might send it to a server. One might keep a protected copy. Another might create a permanent cloud record. One might require deliberate action. Another might automate everything.
“We’ll show you the photo before you open it!”
Another tiny convenience. Someone sends something, and the app automatically loads it so you can see what it is without doing anything.
But automatic means the app is making the decision for you. It is fetching, processing, or displaying something before you have consciously chosen to open it.
And the more kinds of things an app automatically opens, previews, renders, or processes, the more outside material its software has to handle.
“We will show you the message right in your notification!”
Convenient, absolutely. You see who messaged you and sometimes even the message itself without opening the app. But now that private content is being displayed outside the app, on a part of the phone that may be visible from the lock screen or to anyone who can see your notifications.
The message may still be protected inside the app, but the moment its contents appear in a push notification, you have created another place where that information can be seen.
The Real Test of a Privacy-First App
That is the real test of a privacy-first app: not how many times it says “secure,” but how many times its design is willing to inconvenience itself instead of exposing you.
Look at what happens when you say no. Does the app still work? Can you decline contact access? Can you keep backups under your own control? Can you prevent automatic previews? Can you decide where sensitive files are stored? Can you require authentication before someone reaches your conversations? Can you understand what leaves your device and why?
Those answers tell you far more than a shield icon ever will.
Because privacy is not a feeling an app gives you. It is a set of technical decisions made when nobody is watching: what stays on your device, what leaves it, who can decrypt it, how long information survives, what third parties receive, what the app does automatically, and how much control remains in your hands.
Good privacy features are not just about adding more locks or stronger encryption and stopping there. With these, they are about making thoughtful choices and giving users control over what is absolutely theirs.
That is what privacy by design really looks like. And once you start looking at privacy risks in apps this way, the preferences change.
It is all about which app gives you the most control while keeping data collection at zero, rather than quietly collecting or using your information behind the scenes.